Evaluate the local control honestly
Cloud Secure may fit selected supported-provider sync-folder access workflows on a Windows PC after current-version testing. It restricts local access; it does not provide provider-side encryption, Google Drive account recovery, link control, MFA, permission bypass, guaranteed backup or full-device security.
An scholarship board administrator prepares a fictional scholarship-file package on an approved Windows review laptop, tests the relevant layer and keeps the working source separate.
Run the control sequence
- 01
Verify the official installer, license, current release and supported Google Drive client.
- 02
Pilot with fictional scholarship applications on the intended Windows profile.
- 03
Test lock, unlock, sign-out, restart, sync and offline behavior.
- 04
Inspect temp files, downloads, previews and alternate local paths.
- 05
Approve only the verified local use and document provider-side controls separately.
Preserve decision evidence
Record product and client versions, Windows build, protected path, test manifest, lock results, residue, provider controls, backup and owner.
Stop when
- Legacy artwork is treated as proof of current support.
- The product is described as provider-side encryption or account recovery.
- No independent recovery copy or Google Drive permission review exists.
Keep secrets and unnecessary applicant data out of the decision record.
Separate local and provider controls
PC-side folder access is not provider-side encryption, Google Drive account recovery, sharing-link control, MFA, permission bypass, guaranteed backup or full-device security.
Inspect the workflow, not the artwork
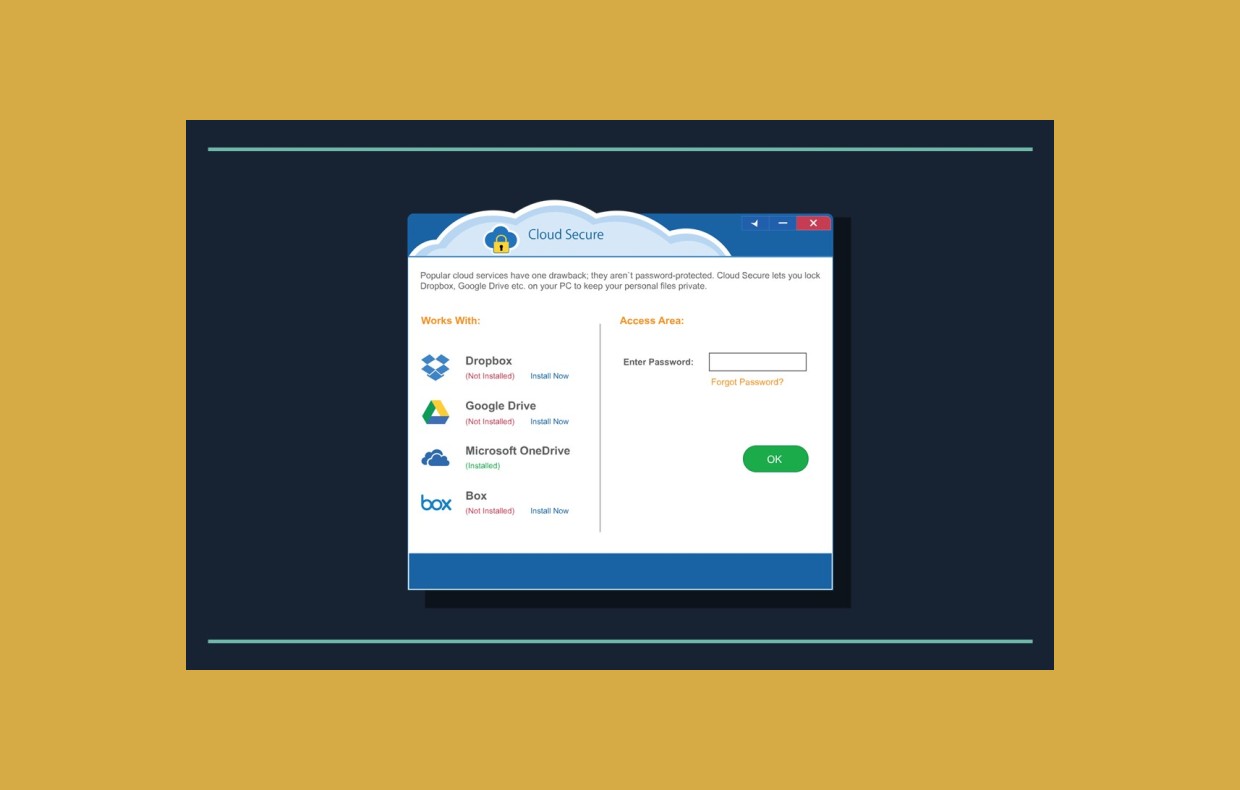
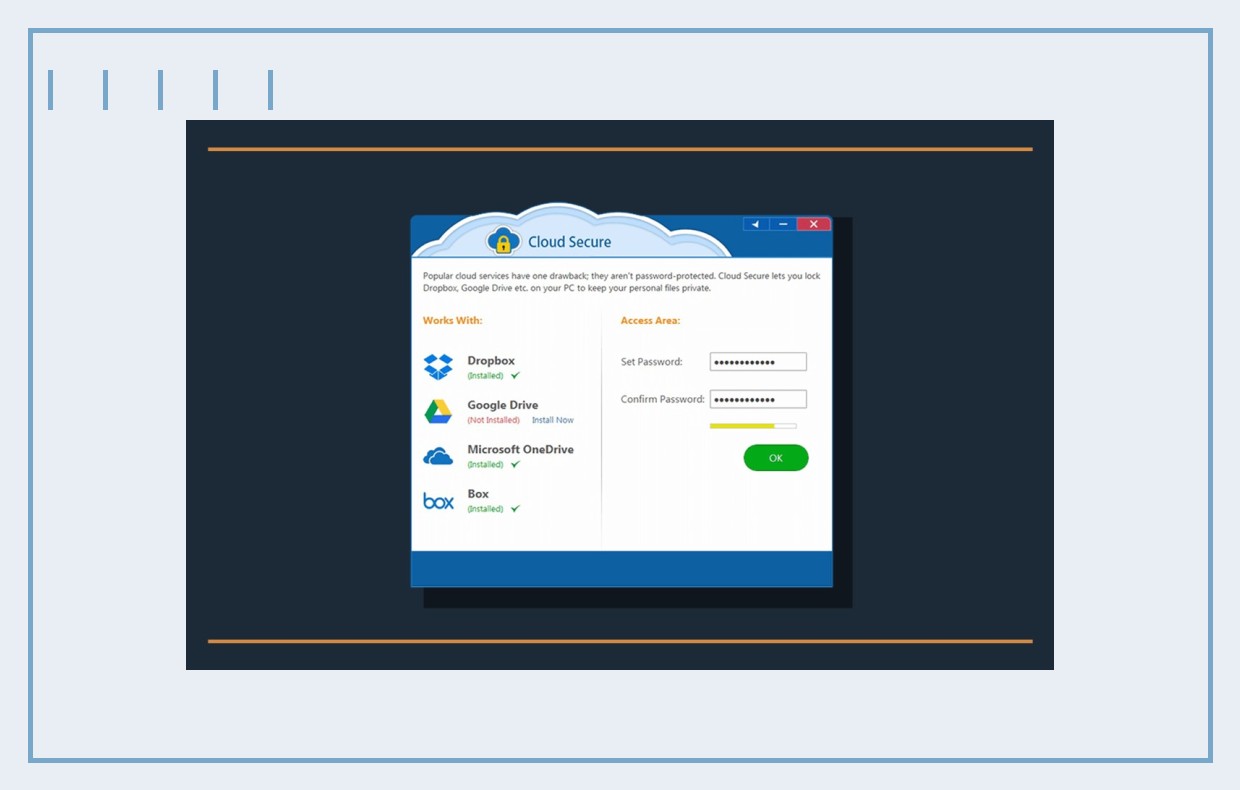
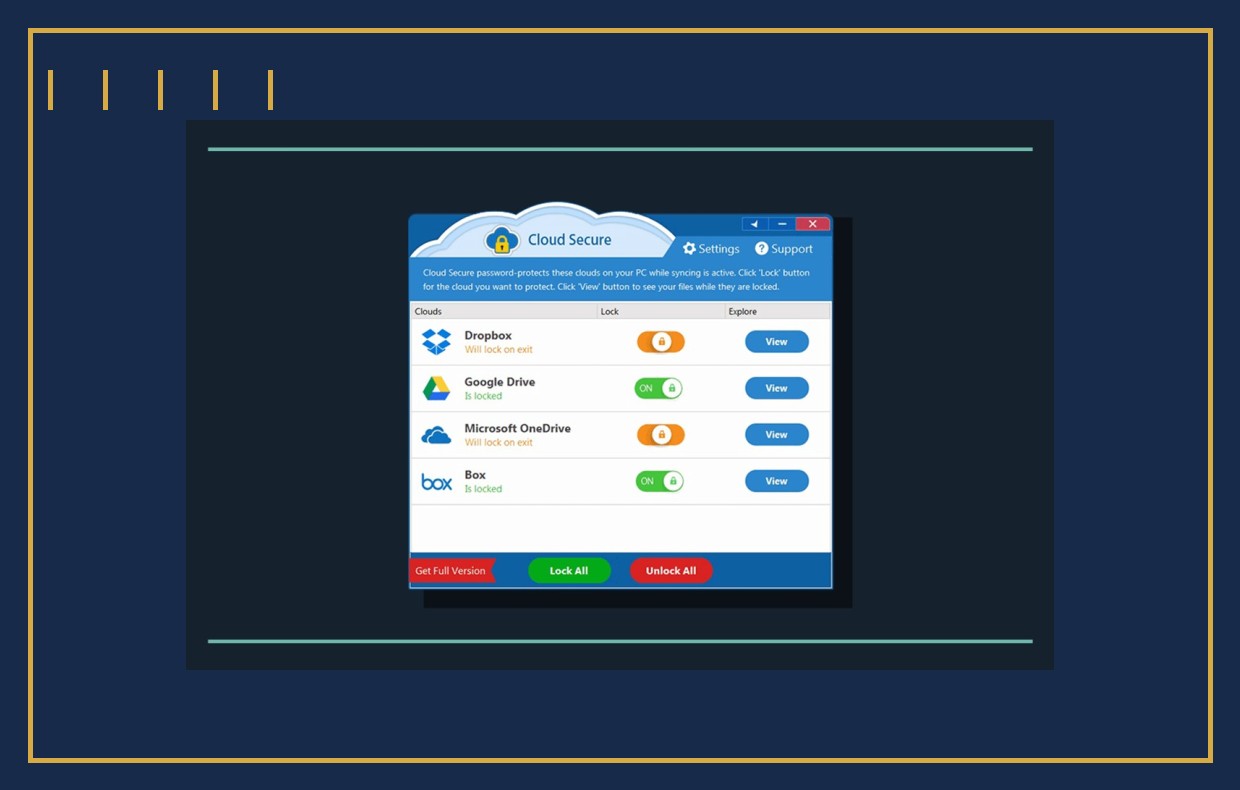
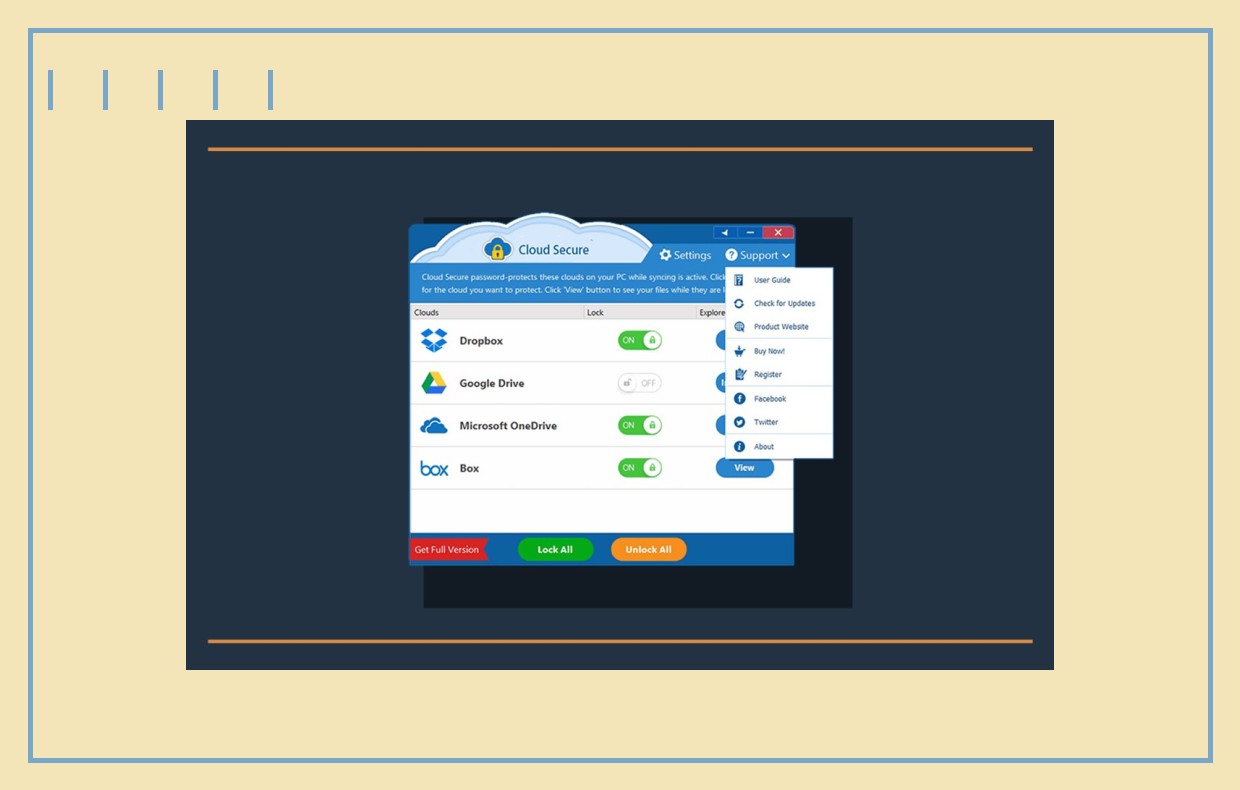
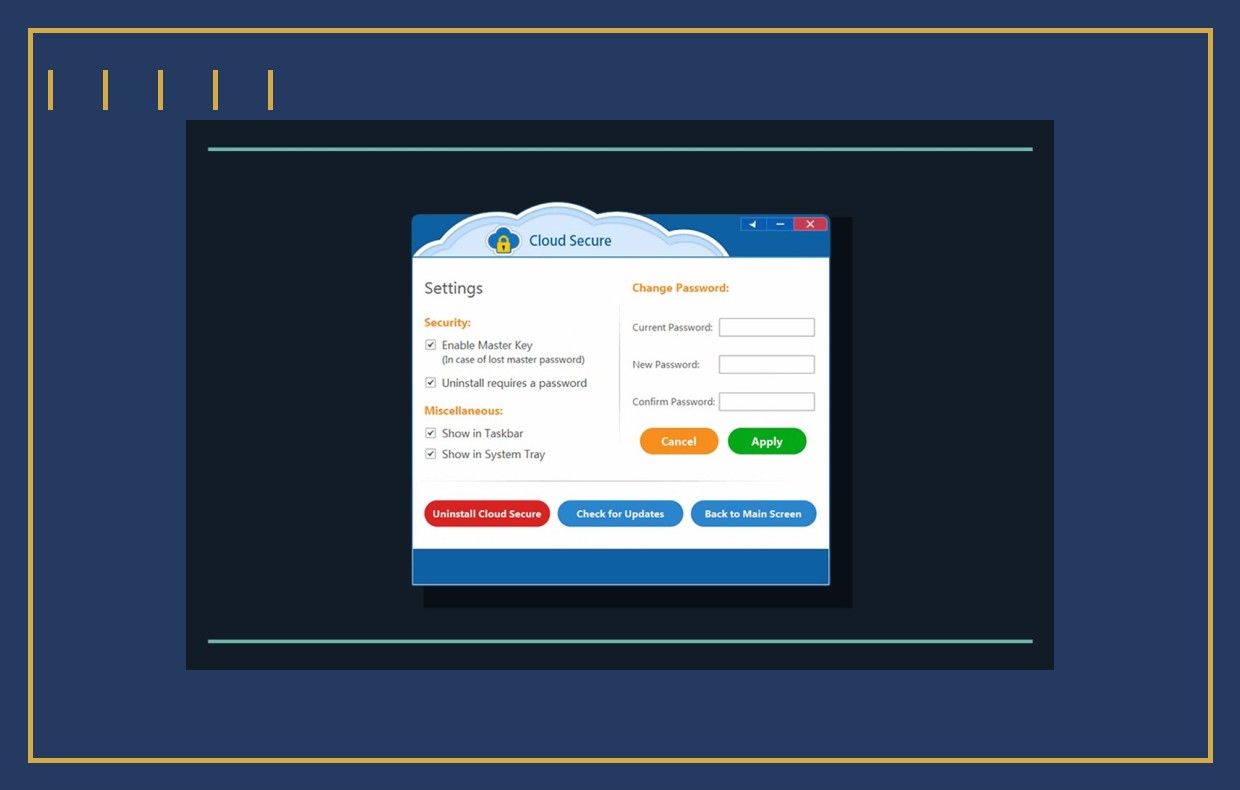
Cloud Secure does not provide provider-side encryption, Google Drive account recovery, sharing-link control, MFA, permission bypass, guaranteed backup or full-device security.
Local sync questions
Does local folder access control the Google Drive account?
No. Google Drive permissions, links, MFA, sessions and recovery remain provider controls.
Is sync an independent backup?
No. Test a separately stored recovery copy outside the same account and device failure domain.
Primary references
References support specific boundaries and do not imply endorsement.